




Build evidence before your first SOC interview.
Getting into a SOC role is hard when your experience is limited to videos and practice questions. SOC Analyst Prep Labs puts you inside a live Splunk environment to investigate alerts, analyze logs, enrich evidence, and write up what happened.
$249 includes 90+ lessons across 12 topics, lifetime access to the course, 12 months of live Splunk lab access, and unlimited attempts on included practice exams.
How you build experience here
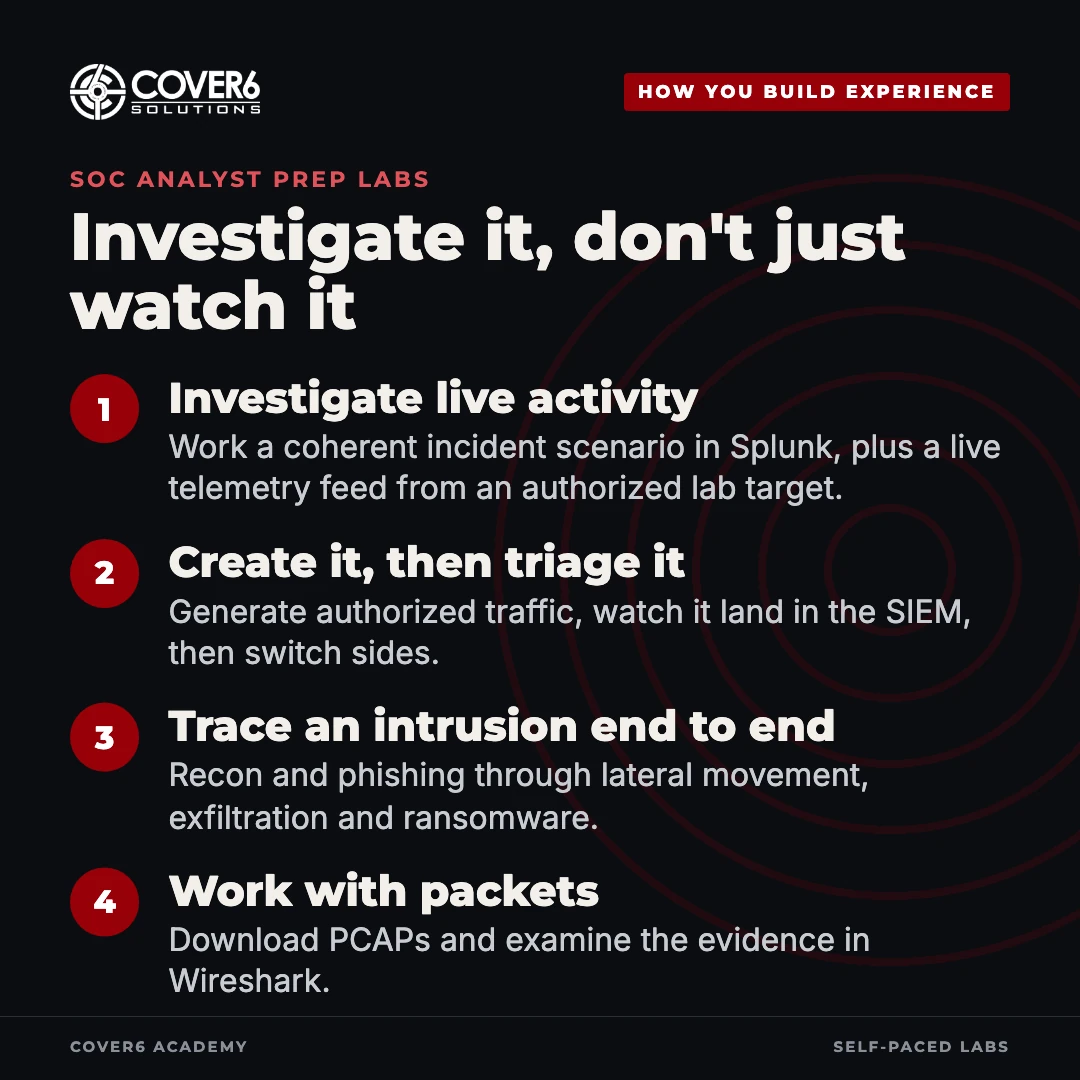
- Investigate live and structured activity. Work from a coherent incident scenario in Splunk, then use a live telemetry feed from an internet-facing authorized lab target to practice finding and interpreting attacker activity.
- Create activity, then investigate it. Generate authorized traffic against the lab target and watch it appear in the SIEM. Then switch perspectives and triage the evidence.
- Trace an intrusion end to end. Follow recon, phishing, execution, persistence, credential theft, lateral movement, command and control, exfiltration, and ransomware through network, endpoint, and log evidence.
- Work with packets, not just screenshots. Download PCAPs and use Wireshark to examine the evidence behind the alert.
What you get
- 90+ hands-on lessons across 12 topics. Learn SOC fundamentals, Splunk, log and network analysis, phishing analysis, incident response, endpoint detection, vulnerability management, compliance, and threat hunting.
- 12 months of live Splunk lab access. Your lab is included with enrollment and can be extended for $99 per year or $19.99 per month after the initial period.
- Hands-on work in every topic. Practice alert triage, timeline reconstruction, threat-intelligence enrichment, dashboard building, endpoint forensics, and threat hunting.
- A verifiable certificate. Complete the course to earn the SOC Analyst, Level II certificate with 17 CPE hours, verifiable at cover6solutions.com/verify.
- Downloadable PCAPs and a full incident report. Complete the investigation and document your conclusion.
Practice exams included
Your enrollment includes practice exams for CySA+, CC, SSCP, and Security+.
Unlimited attempts. Randomized questions. Use your results to see which objectives to revisit while you build hands-on skill.
Course facts
- Level: Intermediate
- CPE: 17 hours
- Course: 90+ lessons across 12 topics
- Lab: 12 months of live Splunk access, extendable
- Practice exams: CySA+, CC, SSCP, and Security+
The 12 topics
- SOC Fundamentals
- Threat Intelligence and the Landscape
- SIEM Architecture and Splunk Foundations
- Log Analysis
- Network Traffic Analysis
- Phishing and Email Analysis
- Incident Detection
- Incident Response
- Endpoint Detection and Response
- Vulnerability Management
- Security Frameworks and Compliance
- Threat Hunting
Who this is for
- You want a Tier 1 or Tier 2 SOC analyst role and need work you can describe clearly.
- You are pursuing certifications and want the hands-on side to match.
- You are changing careers and need a structured way to practice analyst work.
- You already work in IT and are moving into security.
You do not need prior Splunk experience. The course teaches the platform before asking you to use it in an investigation.
Why Cover6
This is practical training built and taught by Tyrone E. Wilson, based on more than a decade of live cybersecurity instruction. The goal is simple: give you work you can explain when someone asks what you have actually done.
FAQ
How long does it take? The course is self-paced. Your course access does not expire, and your lab access runs for 12 months.
Are the Splunk credentials included? Yes. They are emailed automatically after your order completes.
Do I need certifications first? No. The practice exams are included and the course is designed to help you build the skills alongside them.
Will this guarantee a job? No course can promise that. This one gives you real investigation work and a stronger answer when asked about your experience.
Ready to build proof?
Add SOC Analyst Prep Labs to your cart for $249 and begin your first investigation.